CIP-003-9 Automated today
Security Management Controls
CIP-003-9 sets the management controls for cyber security. Cyber security policies must be reviewed and approved by the CIP Senior Manager at least every 15 calendar months (R1). Any entity with low impact BES Cyber Systems must implement a cyber security plan covering the Attachment 1 sections, which now include vendor electronic remote access controls (R2). The CIP Senior Manager must be identified by name, with changes documented within 30 days (R3). Delegations of authority must be documented (R4).
| Status | Effective April 1, 2026 |
|---|---|
| U.S. effective date | April 1, 2026 |
| Policy review (R1) | Every 15 calendar months, approved by the CIP Senior Manager |
| New in -9 | Attachment 1 Section 6: vendor electronic remote access security controls for low impact BES Cyber Systems |
| CIP Senior Manager (R3) | Named; changes documented within 30 calendar days |
| Next versions | CIP-003-10 (July 1, 2028), CIP-003-11 (July 1, 2029) |
| Related | CIP-002-5.1a, CIP-004-7 |
What CIP-003-9 requires
Our plain-language summary of each requirement. The standard's text governs.
Policies
Review and obtain CIP Senior Manager approval at least every 15 calendar months for documented policies covering the required topics for high, medium and low impact systems.
Low impact plan
Implement documented cyber security plans for low impact BES Cyber Systems that include the sections in Attachment 1: awareness, physical and electronic access controls, incident response, transient cyber assets and removable media, and vendor electronic remote access.
Name the CIP Senior Manager
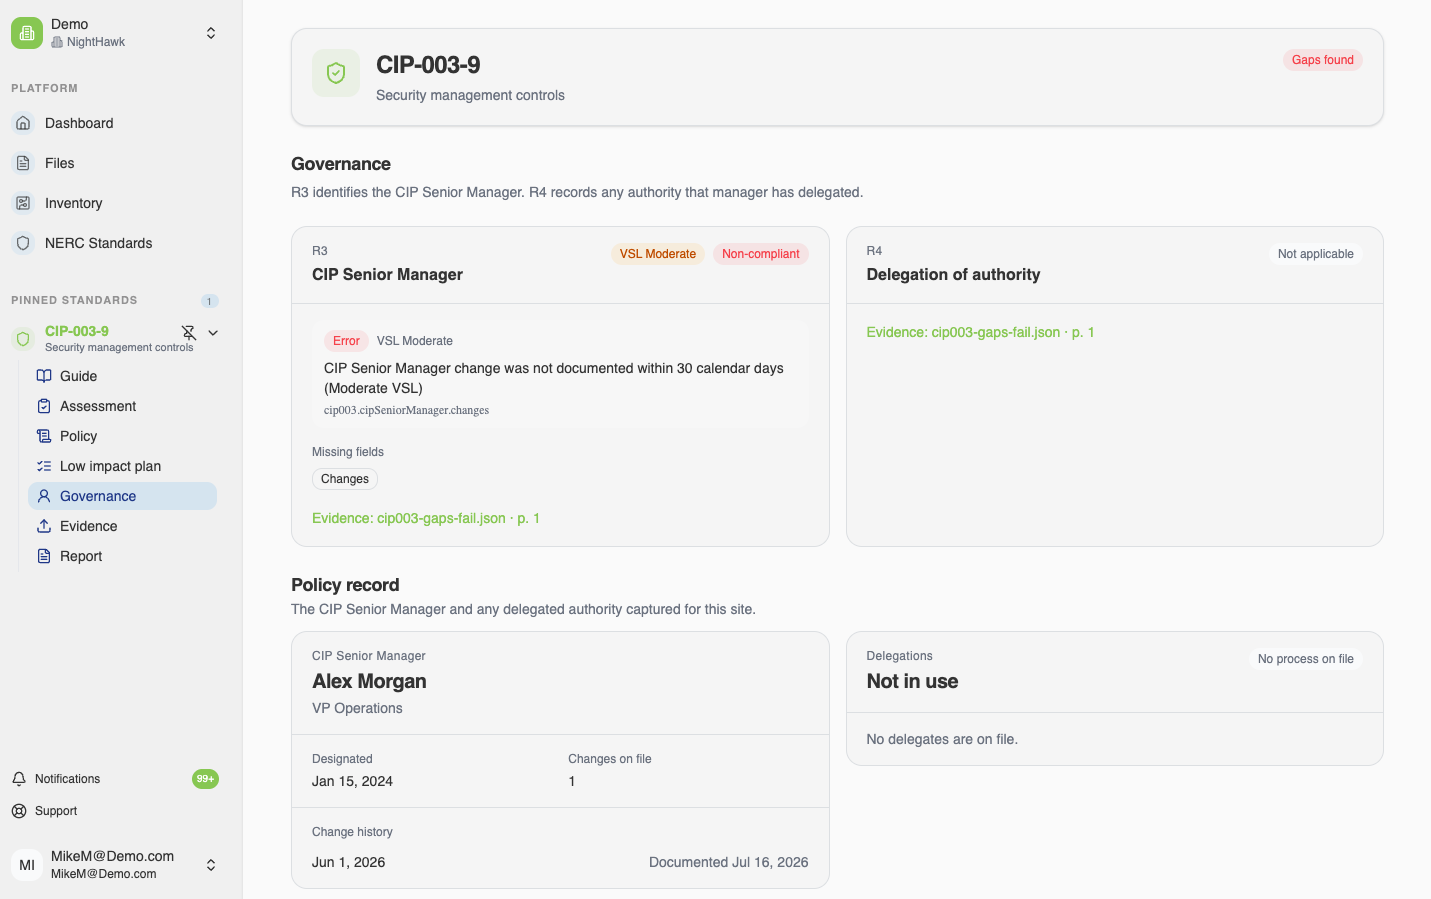
Identify the CIP Senior Manager by name and document any change within 30 calendar days.
Delegations
Implement a documented process to delegate authority, recording the delegate's name or title, the actions delegated and the date.
Evidence an auditor will ask for
- Policies with dated CIP Senior Manager approvals within 15 months
- The low impact plan, section by section, with implementation evidence
- CIP Senior Manager identification and change records
- Delegation records
Where teams get caught
- Section 6 vendor remote access controls not yet documented
- A leadership change documented on day 45
- Low impact plans that differ site to site with no single view
What data phleet does for CIP-003-9
- Tracks R1 policies for required topics, review dates and approval within 15 months
- Reviews the low impact plan section by section for required content, including Section 6 vendor remote access
- Verifies the CIP Senior Manager record and the 30-day change rule, and records delegations
- Flags every gap with its VSL, linked to the source evidence
CIP-003-9 questions
What's new in CIP-003-9?
Attachment 1 Section 6, which requires low impact entities to implement controls for vendor electronic remote access. CIP-003-9 became effective in the U.S. on April 1, 2026.
How often must CIP security policies be approved?
At least once every 15 calendar months, by the CIP Senior Manager.
Other standards we cover
- PRC-005-6 Protection System Maintenance
- PRC-019-2 Voltage Regulating Controls Coordination
- PRC-024-4 Frequency and Voltage Protection Settings
- PRC-025-2 Generator Relay Loadability
- PRC-028-1 IBR Disturbance Monitoring
- PRC-029-1 IBR Ride-through
- PRC-030-1 Unexpected IBR Event Mitigation
- FAC-008-5 Facility Ratings
- CIP-002-5.1a BES Cyber System Categorization
- CIP-004-7 Personnel and Training
- Inventory Asset Inventory
See your CIP-003-9 evidence, organized.
Book 30 minutes. Bring one site's records and we'll surface the evidence live, show you the gaps and walk through the reports.