CIP-004-7 Automated today
Personnel and Training
CIP-004-7 covers the people who can reach high and medium impact BES Cyber Systems. It requires a security awareness program (R1), role-based cyber security training (R2), personnel risk assessments (R3), access management with authorization and periodic review (R4), timely access revocation (R5), and, since version 7, a separate access management program for provisioned access to BES Cyber System Information (R6).
| Status | In effect (CIP-004-8 effective July 1, 2028) |
|---|---|
| Applies to | Responsible Entities with high and medium impact BES Cyber Systems |
| Programs | Awareness, training, personnel risk assessment, access management, revocation, BCSI access |
| New in -7 | R6: authorize, verify and revoke provisioned access to BCSI |
| Next version | CIP-004-8, U.S. effective July 1, 2028 |
| Related | CIP-002-5.1a, CIP-003-9 |
What CIP-004-7 requires
Our plain-language summary of each requirement. The standard's text governs.
Security awareness
Documented processes that reinforce cyber security practices, per Table R1.
Training
A role-based cyber security training program covering the Table R2 topics, completed before access and at the required interval.
Personnel risk assessment
A documented PRA program for authorized electronic or unescorted physical access, per Table R3.
Access management
Authorization based on need, with periodic verification of access, accounts and privileges, per Table R4.
Access revocation
Timely removal of access on termination and reassignment, per Table R5.
BCSI access
Authorize, verify and revoke provisioned access to BCSI, per Table R6.
Evidence an auditor will ask for
- A personnel matrix showing each person's electronic, unescorted physical and BCSI access
- Training, awareness and PRA records with dates
- Authorization records and periodic access reviews
- Revocation tickets with timestamps against the triggering event
Where teams get caught
- HR, IT and security each holding one piece of the record
- Contractors and vendors missing from the roster
- Revocations that miss the deadline because the hand-off was manual
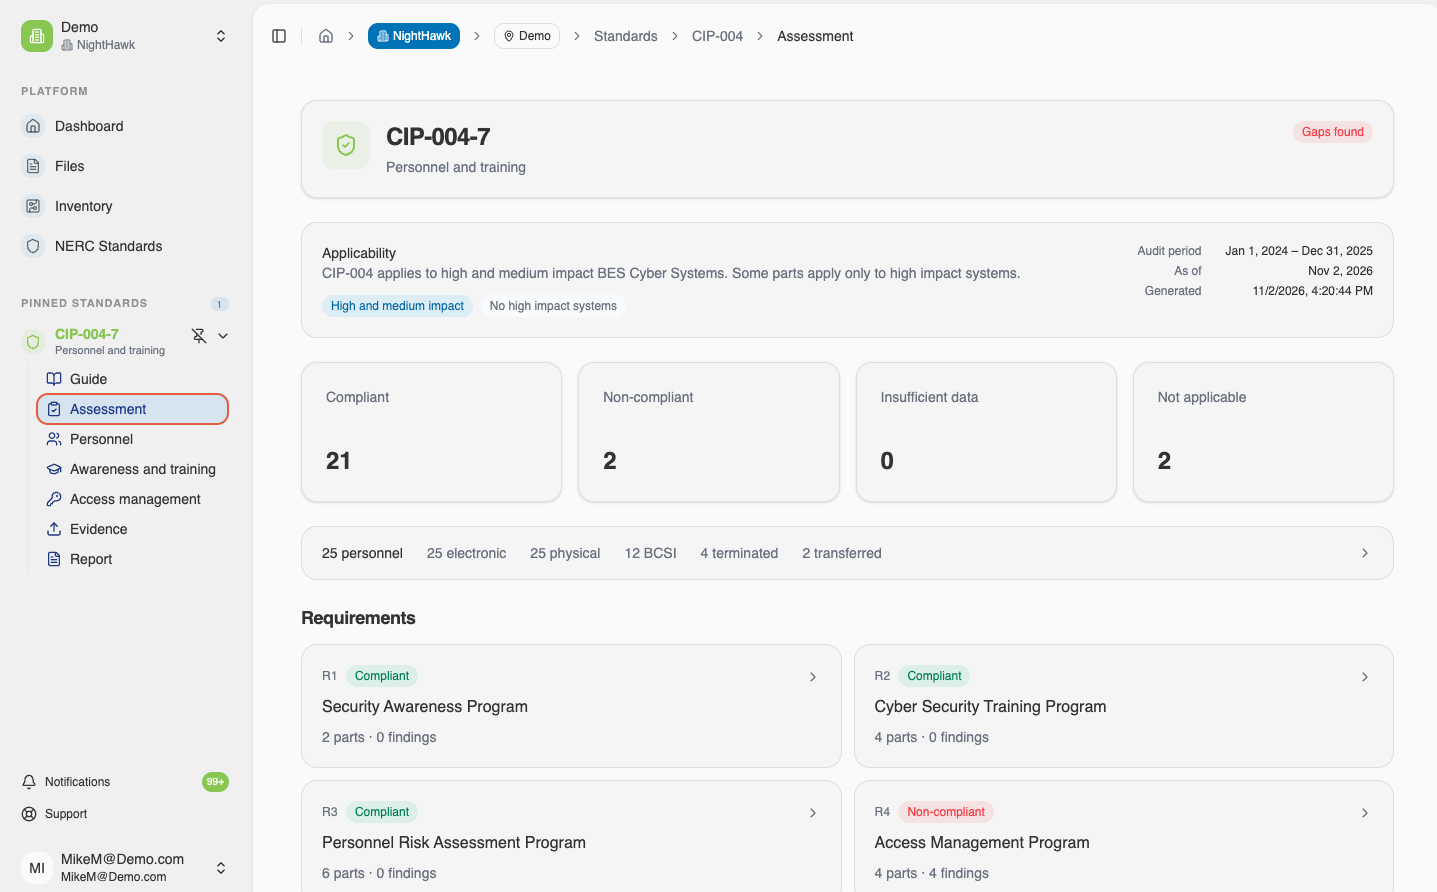
What data phleet does for CIP-004-7
- Builds one personnel roster covering employees, contractors and vendors, with every access type
- Flags each person's lapsed awareness, training, PRA, access review or late revocation
- Confirms a documented program is on file for each requirement
- Flags gaps part by part and generates a report with the full personnel matrix
CIP-004-7 questions
What is new in CIP-004-7?
Requirement R6, which moves management of provisioned access to BES Cyber System Information (BCSI) into its own requirement to authorize, verify and revoke that access.
Other standards we cover
- PRC-005-6 Protection System Maintenance
- PRC-019-2 Voltage Regulating Controls Coordination
- PRC-024-4 Frequency and Voltage Protection Settings
- PRC-025-2 Generator Relay Loadability
- PRC-028-1 IBR Disturbance Monitoring
- PRC-029-1 IBR Ride-through
- PRC-030-1 Unexpected IBR Event Mitigation
- FAC-008-5 Facility Ratings
- CIP-002-5.1a BES Cyber System Categorization
- CIP-003-9 Security Management Controls
- Inventory Asset Inventory
See your CIP-004-7 evidence, organized.
Book 30 minutes. Bring one site's records and we'll surface the evidence live, show you the gaps and walk through the reports.